Keep Your Funds
Safe From Here On
Safeheron offers enterprise-grade digital asset self-custody services and MPC privatization solutions, ensuring the highest level of security for your assets.
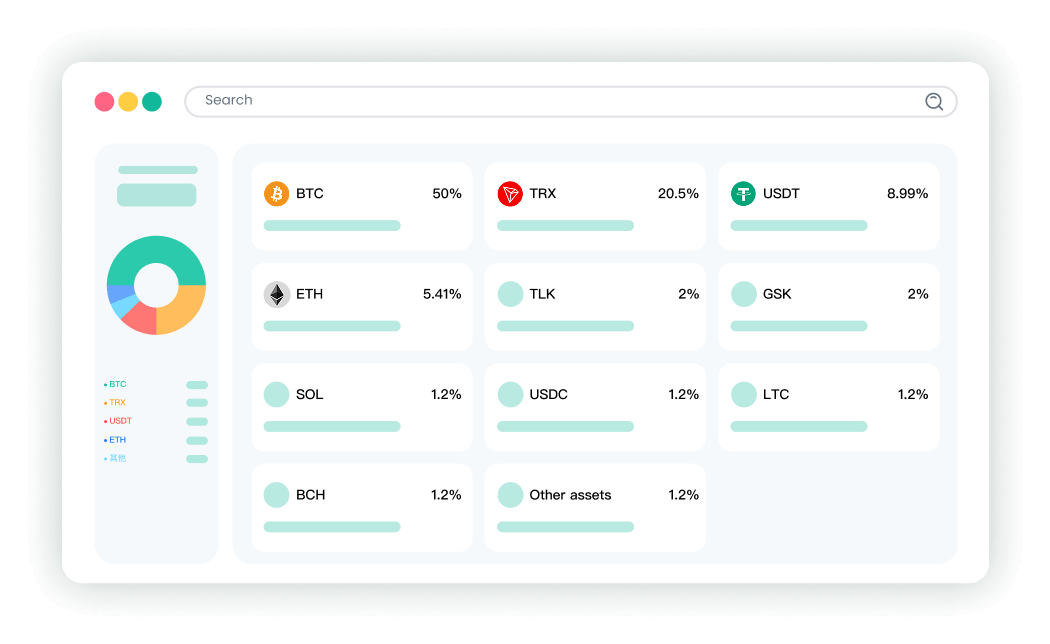
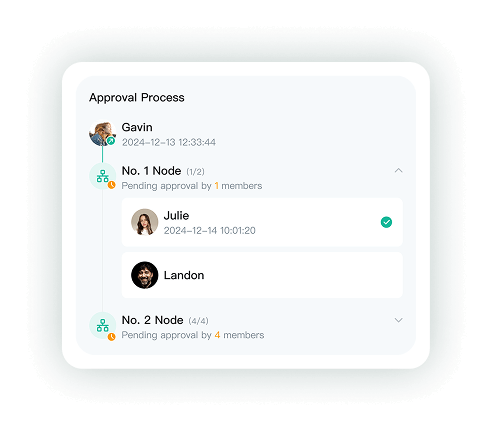
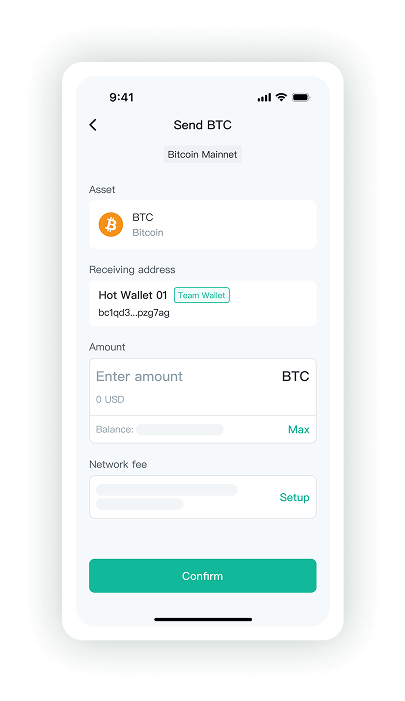








Secure, Efficient, Scalable
Top-tier, battle-tested security solutions for 280+ institutions since 2021.
RAISED
PEAK AUC
SECURELY TRANSFERRED
Committed to the highest standards of security and compliance.
Certified and Insured
Partner with Top Security and Compliance Partners
Compliance in Action
 Explore Our Trust Center
MPC Self-Custody
Enterprise-grade digital asset self-custody services
Eliminate single-point failures to manage digital assets
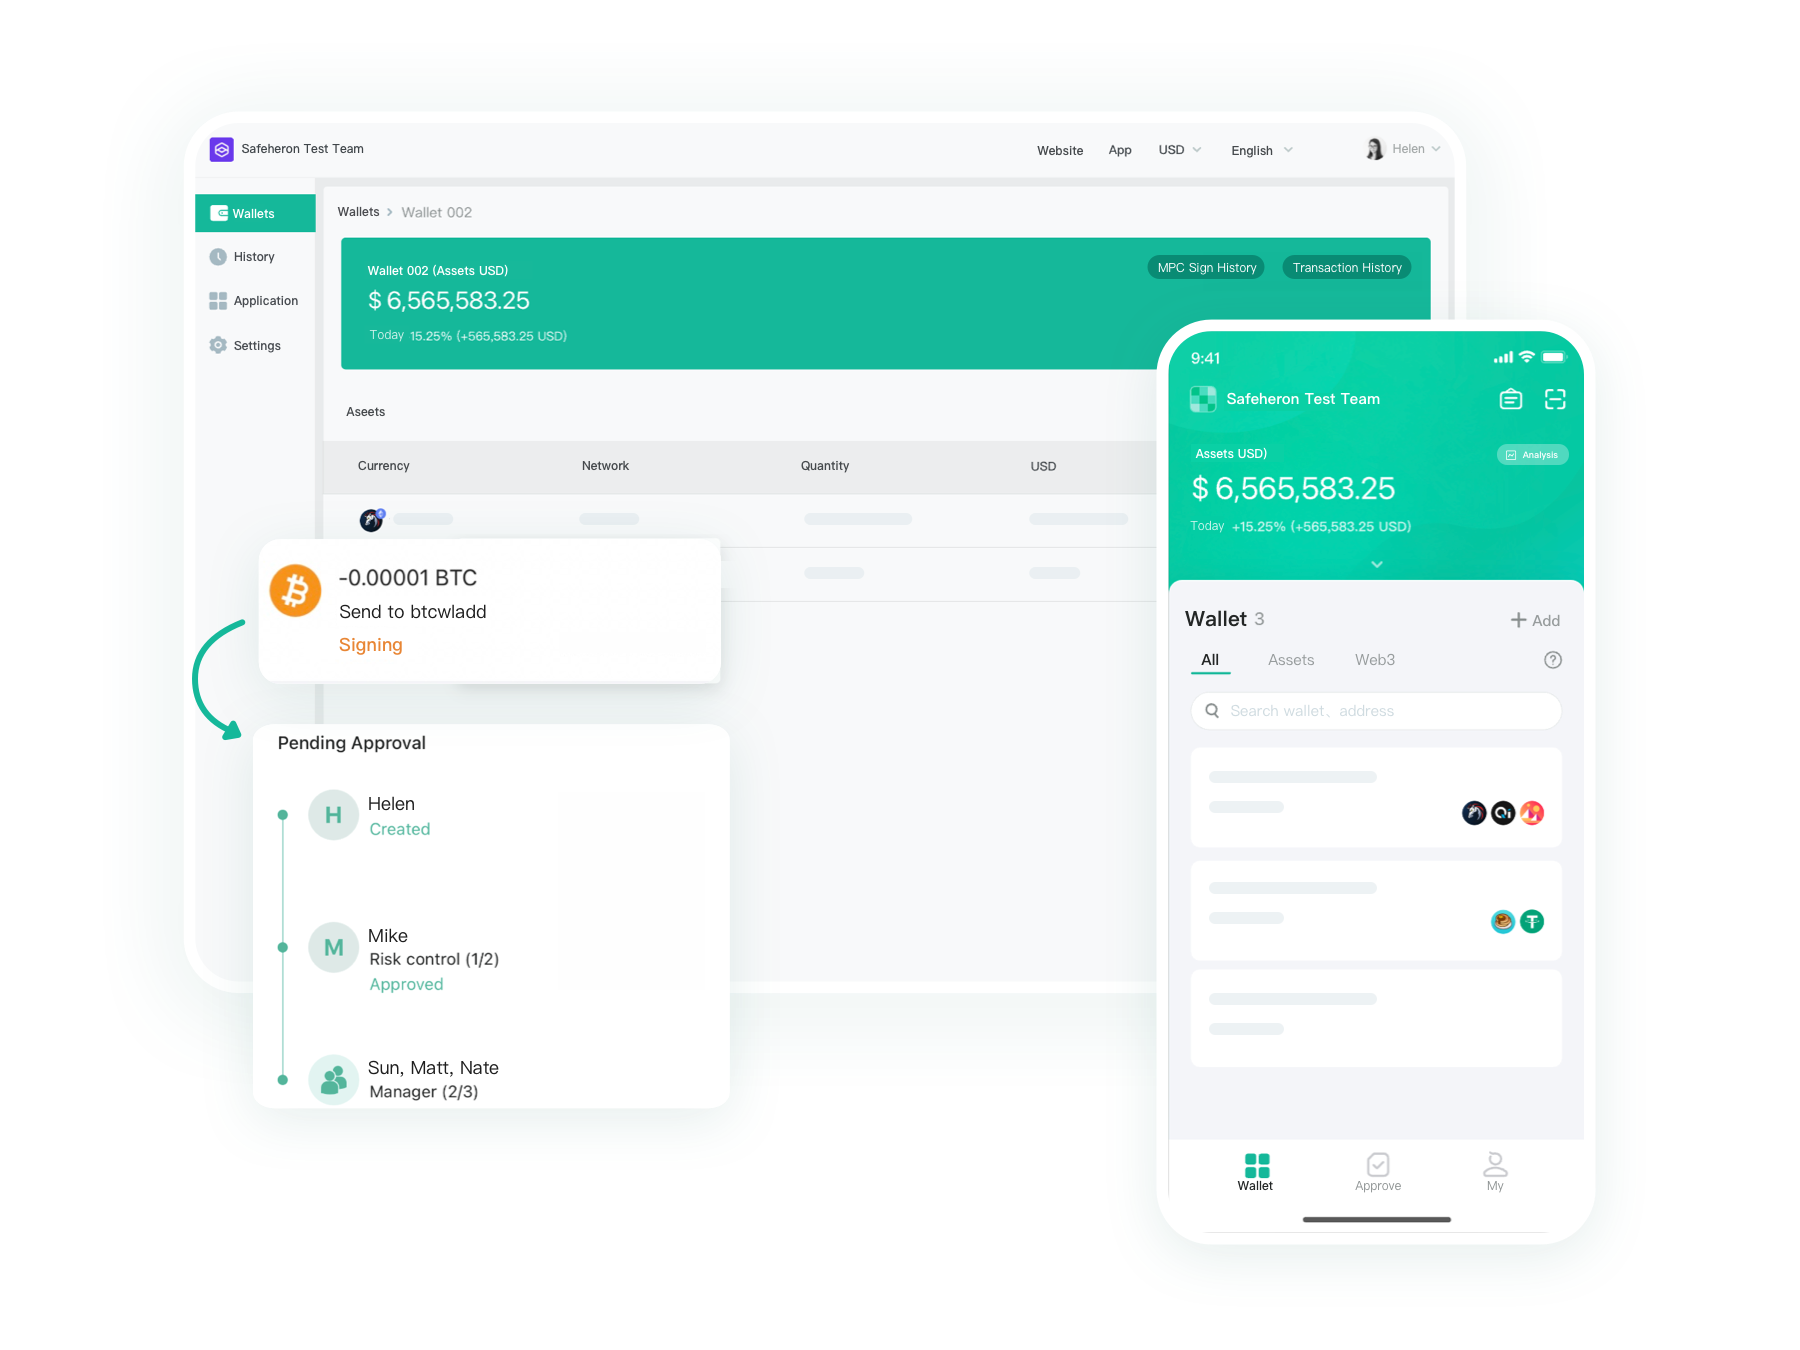
- MPC and TEE technologies protect your digital assets with the highest level of security.
- Manage wallets and transfer funds on multiple terminals, including the mobile App and Web Console.
- Policy Engine flexibly controls access authorization.
- Off-chain multisignature enhances approval privacy and significantly reduces on-chain transaction fees.
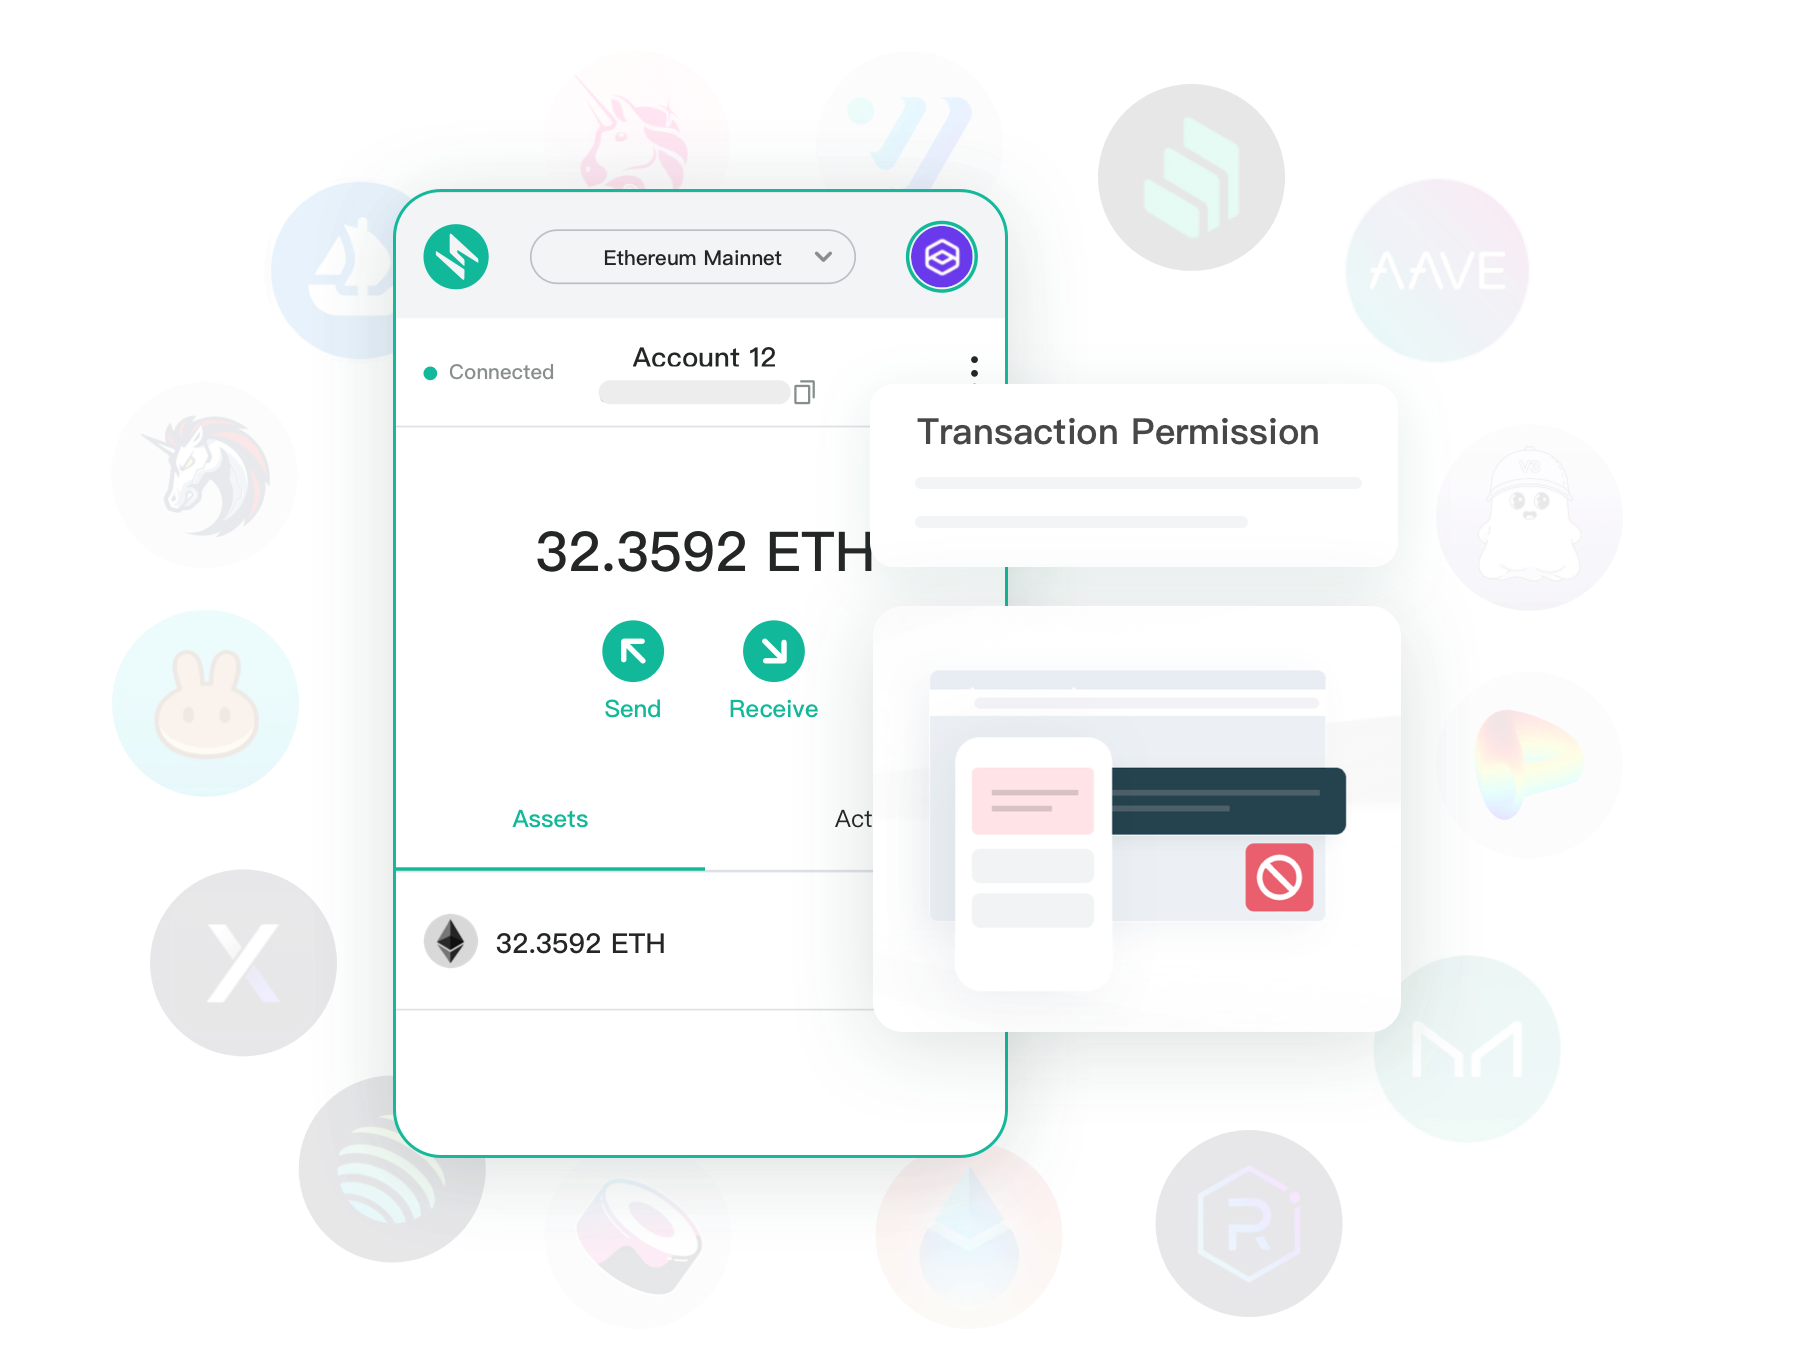
Interact with dApps under multi-party control
- Supports all public EVM-compatible blockchains and DeFi protocols.
- Policy Engine meticulously delegates transaction permissions.
- Real-time contract monitoring and phishing detection safeguard every transaction.
- Customize RPC nodes for diverse business scenarios.
- Collaboratively manage smart contract owner’s permissions to reduce single-point risk in critical operations.
Enterprise-grade digital asset self-custody services
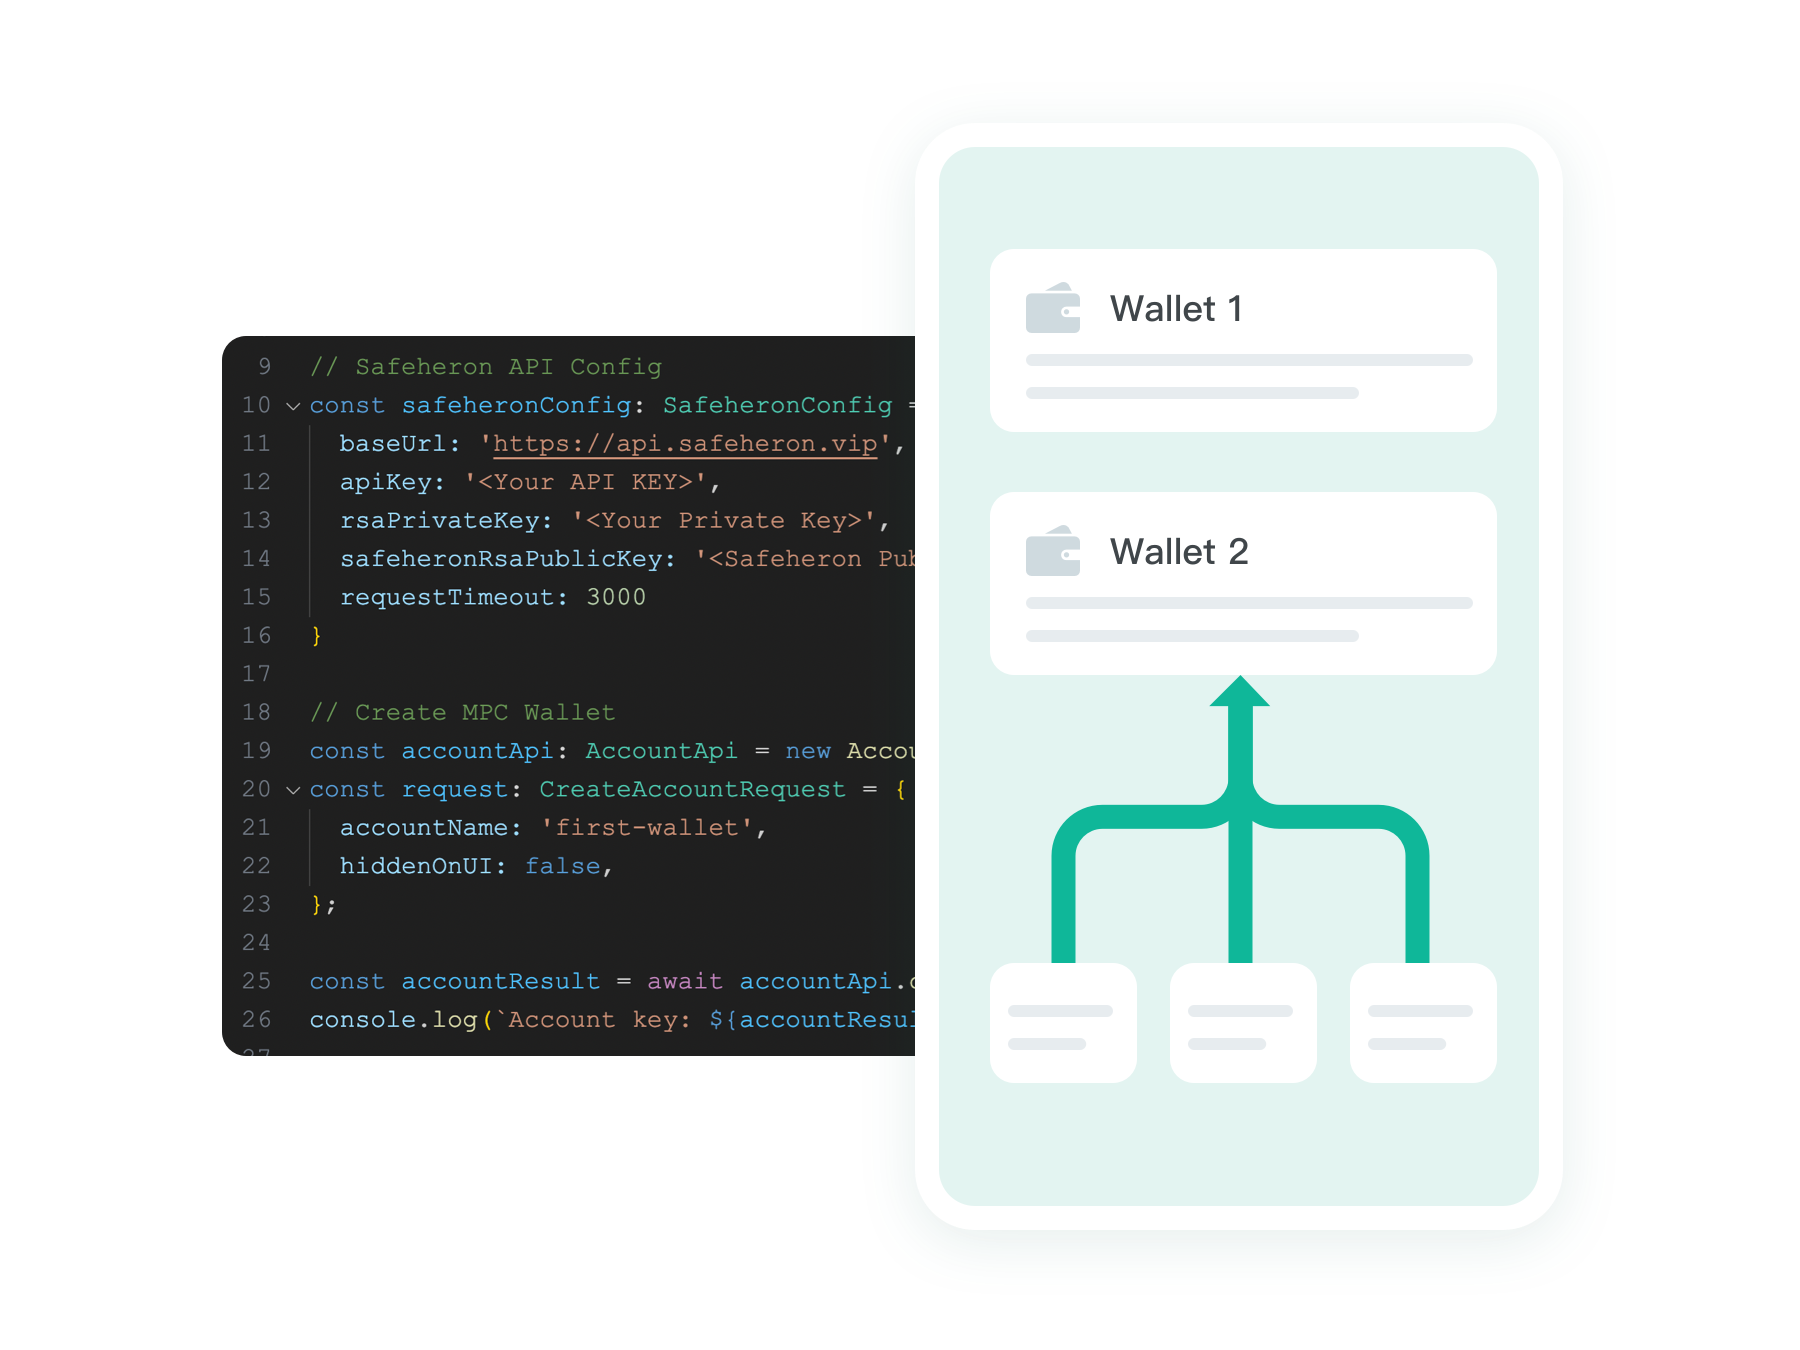
- Seamlessly create and manage millions of MPC wallets with APIs.
- Automatic gas fuelling and sweeping significantly improve integration efficiency and accelerate your business success.
- Web3 API securely controls the entire lifecycle of smart contracts.
- API Co-Signer automates transaction approval and signing.
- MPC and TEE technologies provide multi-layer security to eliminate single-point-of-failure risk for private keys.
MPC Node Suite
White-label MPC privatization solutions
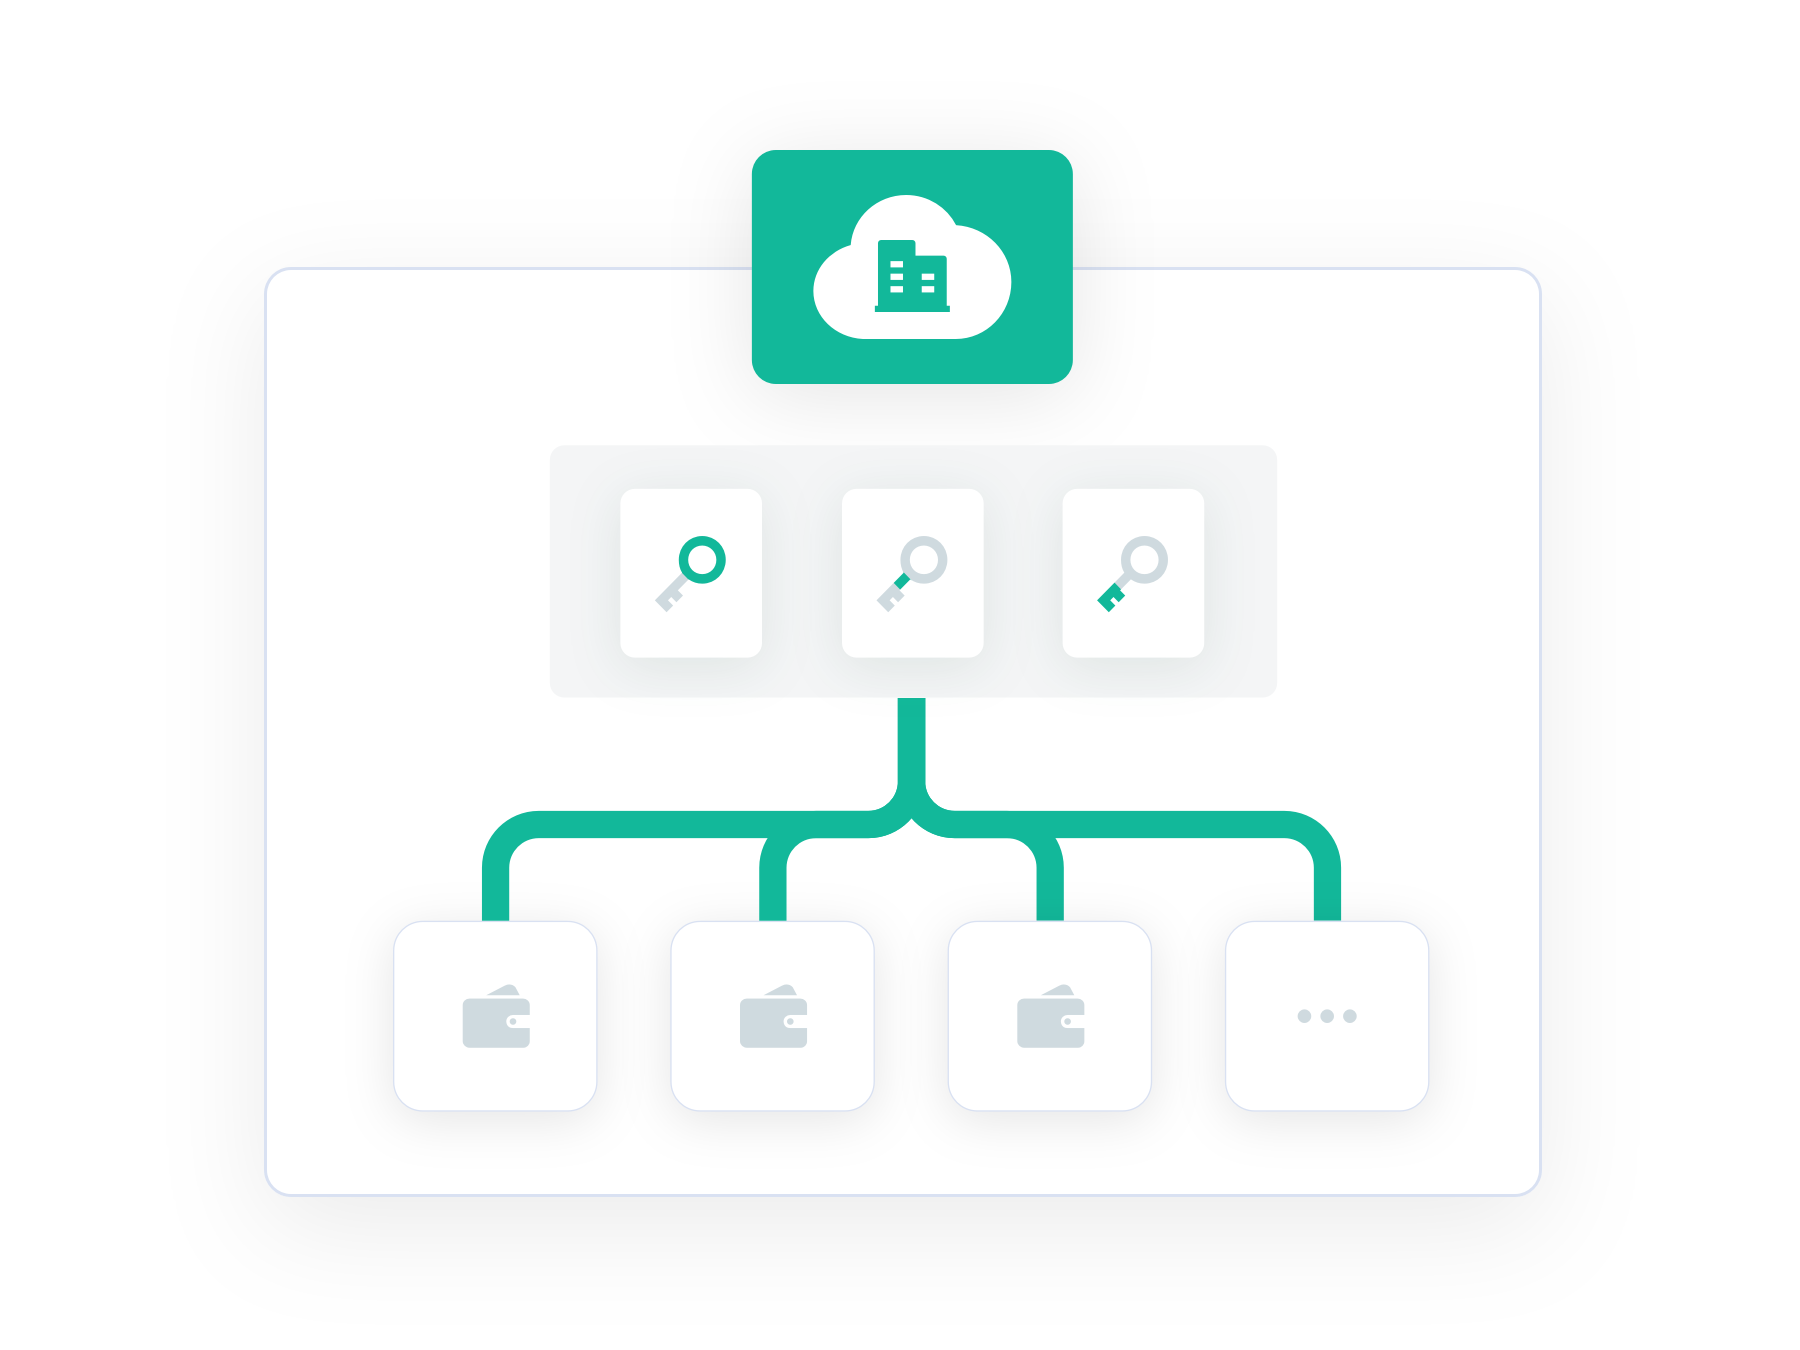
Flexibly build MPC wallets for seamless integration into your applications
- Fully privatized, with hardware-level data security and privacy protection under your control.
- A secure, universal, and cross-platform MPC-TSS key management solution.
- Support diverse business scenarios to accelerate your success.
Safest software is
open source
Safeheron independently developed MPC algorithms and is now the world's first company to open-source the mainstream MPC-TSS algorithm in C++.
Why choose us?
100% control over assets
3-of-3 MPC-TSS key management eliminates the single-point failures with full asset control.
Open-source algorithms
Safeheron open-sourced the world's first MPC-TSS algorithm library implemented in C++.
Maximum security
Safeheron’s multi-layer security defenses against state-level attacks.
Certified and insured
Safeheron is certified with ISO/IEC 27001:2022 and SOC 2 and is insured by Lockton.
Extensive features
Safeheron offers one-stop management for Web3, DeFi, NFTs, and smart contracts.
Governance and policy
TEE Policy Engine customizes multi-dimensional policies and approval workflows.
Technical support
Robust technical support encompasses use cases, solutions, technologies, and security expertise.
Diversified solutions
Battle-tested SaaS services and MPC privatization solutions.
Hear from our customers
Our partnership with Safeheron has unlocked new possibilities in digital payment through advanced MPC and TEE technology. This collaboration strengthens our security, scalability, and compliance, enabling us to meet the highest standards. With Safeheron’s powerful MPC self-custody solution, dtcpay continues to provide our users with institutional-grade security, seamless transactions, and an intuitive user experience, reinforcing our commitment to advancing the future of digital payments.
As a trusted financial service provider, we have strict standards when choosing our security infrastructure provider. Safeheron turns out to be a great match. Its MPC self-custody solution eliminates private key risks while providing enterprise-grade security with ease of use. With Safeheron’s sophisticated technology, we are confident to provide our customers with a reliable and secure digital payment experience.
The Safeheron team has in-depth expertise and extensive practical experience in blockchain security. With a highly robust security mechanism, a comprehensive permission management system, and an excellent user experience, Safeheron has provided strong support for our institutional trading services in the Asia region. We look forward to further deepening our collaboration.
UXUY has developed a highly secure key management service powered by Safeheron's MPC technology. In today's challenging cyber environment where digital assets face numerous security threats, Safeheron's mature solution provides us with robust technical assurance. Through this innovative MPC solution, we have effectively reduced the risks of private key leakage and asset theft, delivering users a seamless experience that combines both security and convenience.
With Safeheron’s hardcore MPC technology, we ensure the highest level of security for our clients' crypto funds within our crypto-to-fiat feature. In addition, Safeheron's customer support exemplifies excellence, promptly resolving issues to maintain our uninterrupted operations.

Partnering with Safeheron has been transformative for AlphaYield. Their MPC + TEE platform delivers the enterprise-grade security and operational efficiency we need to execute large institutional trades with complete confidence, while their exceptional team consistently goes above and beyond to support our evolving needs.

Security, flexibility, and compliance — all solved on one platform. Since integrating Safeheron, our business volume has tripled.
Latest Updates from Safeheron


Why Should You Check a Crypto Custody Provider’s SOC 2 Report?
You should check a crypto custody provider’s SOC 2 report because it is issued by an independent auditor and shows whether the provider’s internal controls are suitably designed and whether they have operated effectively over a period of time, rather than being just a promise on its website. For businesses that entrust private keys and assets to a custodian, this report is one of the most direct pieces of third-party evidence when choosing a provider. That said, SOC 2 covers only organization-level controls, so understanding its scope and limitations matters just as much. What Is a SOC 2 Report? A SOC 2 report is an attestation report issued by a certified public accountant on a service organization’s internal controls. The American Institute of Certified Public Accountants (AICPA) defines SOC (System and Organization Controls) as a suite of services that CPAs can provide, and the official SOC 2 guide is titled “SOC 2® Reporting on an Examination of Controls at a Service Organization Relevant to Security, Availability, Processing Integrity, Confidentiality, or Privacy”. As the title suggests, SOC 2 examines controls relevant to security, availability, processing integrity, confidentiality and privacy. These five areas are what are commonly called the Trust Services Criteria. A provider does not necessarily include every one of them in the audit scope, so the first thing to do […]
What Is a Hardware Security Module (HSM)?
A hardware security module (HSM) is a physical computing device dedicated to safeguarding and managing cryptographic keys and performing cryptographic operations internally. The US National Institute of Standards and Technology (NIST), in SP 800-57 Part 2, defines it as “a physical computing device that safeguards and manages cryptographic keys and provides cryptographic processing”, and notes that an HSM is or contains a cryptographic module. NIST gives a more specific description in SP 1800-16: an HSM safeguards and manages digital keys and other secrets in a tamper-evident and intrusion-resistant way, while also providing cryptographic processing. How Does an HSM Protect Keys? An HSM keeps both the storage and the use of keys inside a protected physical device. Applications ask the device to perform cryptographic operations instead of extracting the key and computing on their own. This is why NIST describes an HSM as a device that “safeguards and manages keys and provides cryptographic processing”. At the physical level, NIST SP 1800-16 emphasizes that HSMs are tamper-evident and intrusion-resistant. For modules at higher security levels, FIPS 140-2 also requires tamper response circuitry: as soon as it detects that the enclosure has been opened or a maintenance access interface has been accessed, it immediately zeroizes all plaintext secret keys, private keys and critical security parameters. At the access control level, cryptographic module standards […]
How Does MPC Work?
MPC (secure multi-party computation) works by splitting a secret into multiple shares held by different parties, who use their own shares to complete a computation together, while the complete private key is never reconstructed in any single place. NIST’s threshold cryptography teaching module describes it this way: the secret is split into parts called “shares”, no single share on its own reveals any meaningful information, and cryptographic operations can be carried out without reconstructing the key. Safeheron has already covered the MPC wallet as a product in an article on what an MPC wallet is and how it works. This article focuses on the protocol level: how the key is generated, how signing is completed and how shares are refreshed. What Stages Does MPC Signing Go Through? Over its lifecycle, an MPC-based signing key typically goes through three protocol stages: key generation, threshold signing and share refresh. The key generation stage produces each party’s share, the signing stage uses these shares to produce a signature jointly, and the refresh stage periodically replaces the shares without changing the key. Each of these three stages has a counterpart in published cryptographic research. Gennaro and Goldfeder’s GG18 paper proposed fast threshold ECDSA, including efficient key generation that requires no trusted dealer (dealerless). The CGGMP paper by Canetti, Gennaro, Goldfeder, Makriyannis and Peled added […]
What Is MPC Custody?
MPC custody is a way of safeguarding crypto assets using secure multi-party computation (MPC) and threshold signatures: the private key is split into multiple shares held separately by different parties, the parties compute together when signing, and the complete private key never appears in any single place. The US National Institute of Standards and Technology (NIST) explains in its Threshold Cryptography project that threshold schemes use the principles of secure multi-party computation to distribute trust. For institutions, this means that as long as the threshold is set properly, no single person, single server or single backup can complete a signature alone. How Does MPC Custody Work? MPC custody relies on three stages, distributed key generation, threshold signing and share refresh, to let the parties complete a signature without combining the private key. How MPC works is broken down stage by stage in a separate article. How Is MPC Custody Different from Multisig and HSM Custody? The difference among the three lies in the layer where multi-party control takes place: multisig puts the rules on-chain, MPC places multi-party control in off-chain signing computation, and an HSM protects the key with a hardware boundary. The difference between MPC and HSM, and how the two can be combined, is analysed in a separate article. Is MPC Custody Self-Custody or Third-Party Custody? It can […]
MPC vs HSM: What’s the Difference?
The difference between MPC and HSM lies in how they protect keys: an HSM places the complete key inside a protected physical device, while MPC splits the key into multiple shares held by multiple parties, who compute together when signing, so the complete private key never appears in any single location. The former relies on a hardware boundary to prevent the key from being extracted; the latter relies on cryptographic protocols to distribute trust. In discussions of HSM crypto, the two approaches are often compared side by side, but they are not mutually exclusive, and the same system can use both. How Does an HSM Protect Keys? An HSM protects keys with a dedicated physical device, keeping the complete key within the device boundary, and its security is typically assessed against FIPS 140-3. A hardware security module (HSM) has its own way of working and its own security levels, and it has a distinct role from a key management service (KMS). How Does MPC Protect Keys? MPC (secure multi-party computation) uses cryptographic protocols to distribute trust across multiple parties: signatures are generated collaboratively from multiple key shares, and the private key is never combined in any single location. The process involves specific steps for key generation, threshold signing and share refresh, and MPC wallets and multisig wallets differ in their […]